Wednesday, 27 March 2013

1337Day Inj3ct0rs Official domain hacked - 1337day.com Hacked

1337day official website hacked by  hackers from Morocco with the code names  SQL_Master and Z0mbi3_Ma

With this message in the deface:


Inj3ct0rs Fuck3d !
Hello all ! Today 1337day hacked ! not just for fun or laughing , but sombody from ur team thinks he's the best hacker in the world .
u are sure of ur security :) ?? and u believes no one can hack ur primary domain ( 1337day.com )
and somebody thinks u are the heros :)
now u are been fucked by us , so don't say bullshits again please ;) .
Ass thinks he's a horse :D
We are : SQL_Master and Z0mbi3_Ma


Read more

Sunday, 24 March 2013

Yahoo, LinkedIn, Twitter Accounts Vulnerable to Session Fixation Attacks – Video


Security researcher Rishi Narang has identified a vulnerability that could be exploited by cybercriminals to hijack accounts belonging to Microsoft, Twitter, LinkedIn and Yahoo users. Google and Facebook customers are not impacted by the flaw.

According to the expert, the vulnerability, which can be leveraged to launch session fixation attacks, is caused by an issue with the management of cookies and sessions.

If an attacker can intercept authentication cookies, he can use them to hijack the account because although an expiry date is set, they’re still valid even after the customer logs out.

“The cookie/session ID for an authenticated session is available even after the session has been terminated. There are examples where cookies can be accessible to hijack authenticated sessions,” Narang explained.

“And these cookies are days (sometimes months) old. As a result, someone can successfully access accounts that belong to individuals from different global locations. Even if they would have logged-in/logged out many a times, theirs cookie would still be valid.”


Read more

Sunday, 17 March 2013

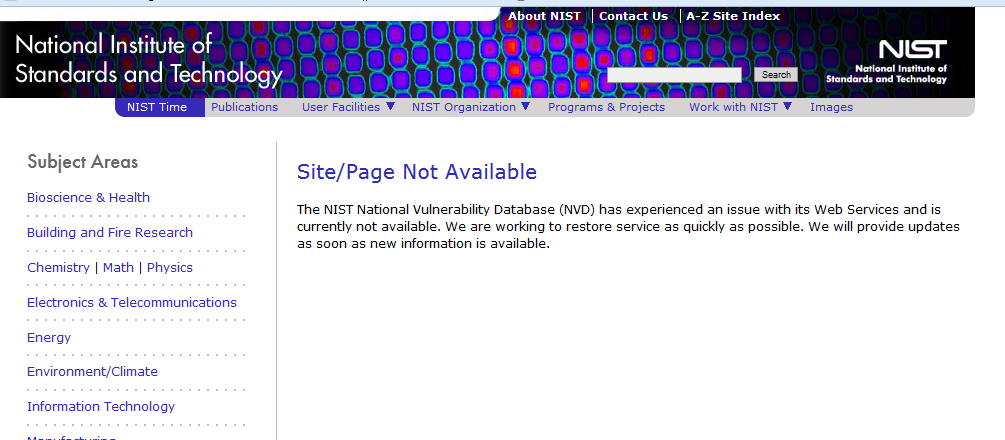
NIST National Vulnerability Database Down, Malware Identified on Two Web Servers

The National Vulnerability Database (NVD) and several other websites operated by the National Institute of Standards and Technology (NIST) have been inaccessible for the past few days.

It turns out that NIST's systems have been hacked. More precisely, the sites have been taken down after malware was identified on a couple of web servers.

Security expert Kim Halavakoski has contacted NIST representatives in an attempt to find out why the NDV is unavailable.

“The National Vulnerability Database public-facing Web site and several other NIST-hosted Web sites are currently unavailable due to discovery of malware on two NIST Web servers,” NIST representatives wrote in an email to Halavakoski, which he posted on his Google+ profile.

“On Friday March 8, a NIST firewall detected suspicious activity and took steps to block unusual traffic from reaching the Internet. NIST began investigating the cause of the unusual activity and the servers were taken offline. Malware was discovered on two NIST Web servers and was then traced to a software vulnerability,” the email continued.

“Currently there is no evidence that NVD or any other NIST public pages contained or were used to deliver malware to users of these NIST Web sites. NIST continually works to maintain the integrity of its IT infrastructure and acts to limit the impact of malware on its systems. We regret the impact this has had on our services.”

Halavakoski makes an interesting observation based on the data provided by NetCraft. Up until March 7, the nvd.nist.gov site was running on Windows Server 2008 and IIS 7.5, but after the breach, starting with March 9, it has been running on Linux and Apache.

NIST representatives state they don’t know when the database will be back online, but they say they will restore it “as quickly as possible.”
Read more

The New Facebook News Feed Is Here and It's Gorgeous

As expected, Facebook unveiled its new News Feed today. Also as expected, it's quite a big change and, perhaps surprisingly for Facebook, look rather slick. Google started caring a lot more about design in recent years and it shows, Facebook seems to finally be doing the same.

But it's more than just the visual aspects, there are plenty of changes to the way the News Feed works, most notably, the fact that it's now split into different sections.

Posts also get more breathing room and, while there are more details, things don't feel cramped.

"You see all the stories you saw in your News Feed before, but with a fresh new look. We've completely rebuilt each story to be much more vibrant and colorful and highlight the content that your friends are sharing," Facebook explained.

But, while you'll still be able to get the full news feed, it's also going to be easier to only focus on the info you want.

There will be four main feeds, one for All Friends, Photos, Music and Following. This segregation makes it possible to check out what your friends are up to without getting flooded by news from your favorite bands.


Another big but obvious change is that the new news feed will be the same on all devices, on the desktop on tablets and on mobile phones.

Everyone will get the new news feed in the coming weeks, both on the site and in the mobile apps.

But if you don't want to wait, you can sign up on the waiting list to get in. Judging by how fast the "queue" for the Graph Search moved, you should be getting the new news feed rather soon.

Naturally, you can expect to hear plenty of complaints from plenty of people as the new news feed rolls out, as with any Facebook update. They will go away soon though.
Read more
 
DMCA.comGags