Sunday, 13 January 2013

Rex Mundi Hackers Blackmail Drake International, Threaten to Leak 300,000 Records


The extortionist hackers from the Rex Mundi collective are back. In the past, they attempted to blackmail Dexia Bank, AmeriCash and Webassur, but now they’ve turned their attention to Drake International, a Canadian job placement firm.

According to the hackers, the company’s systems were hacked last week. They claim to have gained access to 300,000 “confidential job applicant records” and information on the company’s clients.


“We immediately contacted Drake International to offer them not to release the data in exchange of a mere $50,000 (fifty thousand US Dollars). So far, we have unfortunately not heard back from the nice folks over at Drake,” the hackers said.

“Does this mean that they do not care about their clients and job applicants' privacy? You be the judge.”

They warn that if the company fails to make the payment by the end of this week, they will publish the entire database – which includes the details of candidates from Australia, UK, Canada and New Zealand – on Pastebin.

To demonstrate that they’ve gained access to all that data, they’ve published a small sample of job applicant and client details. The sample data includes names, email addresses, passwords, references, phone numbers and other information.

On the other hand, Drake International representatives have told Financial Post that they have no intention of paying the hackers, even though they admit that the hackers have managed to obtain names, email addresses, passwords and phone numbers.

They’re currently working on notifying all the affected individuals, advising them to change their passwords.

The company has also notified the police and they say they’re working with authorities on ensuring that their candidates and clients are protected.

Tony Scala, vice-president of marketing and client service at Drake International, has also revealed that the database breached by Rex Mundi is “very old.”
Read more

User Data at Risk on a Windows 8 – Linux Dual-Boot System


Fast Startup is one of the new features integrated into Microsoft’s Windows 8 operating system that basically allows Windows to boost faster on a dual-boot configuration.

The problem is that the tool puts locally stored data at risk when the user loads the second operating system, in most cases a Linux distribution.

The explanation is as simple as it could be. In dual-boot configurations, the Fast Startup option doesn’t shut down Windows 8 completely, but only forces it to enter a hibernation mode that allows it to reboot a bit quicker when the users sign out from the other operating system.


Since this is nothing more than a hibernation state, Windows 8 will continue to store Windows session information, including file system data belonging to FAT and NTFS partitions.

Even though these system files are actually “locked” in a memory image automatically restored when the user boots back in Windows 8 with Fast Startup, specific files could be easily removed. And here’s why.

The developers behind the ntfs-3g FUSE filesystem driver have discovered that Linux distributions may attempt to write data on Windows partitions as well, sometimes overwriting the system file stored in the memory image we were talking about. When booting back into Windows 8, Fast Startup loads the operating system, but without the missing data.

In order to overcome this problem, the software creators have introduced an update that would require any Linux distribution to mount NTFS partitions as read-only and thus block any attempt to overwrite system data locked by Fast Startup.

According to H Online, however, an official release of the ntfs-3g driver with these modifications is yet to be launched, so Windows 8 – Linux dual-boot configurations are still vulnerable to this issue.

In addition, most Linux distributions on the market, including Ubuntu, Debian and openSUSE are yet to address this problem, so blocking the operating system from overwriting Fast Startup data is impossible for the time being.
Read more

Aaron Swartz, Reddit Co-Founder, Dead in Apparent Suicide


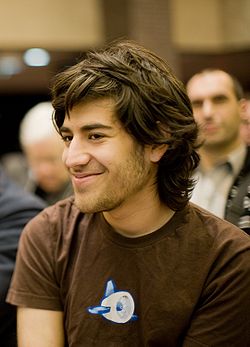
Aaron Swartz, the 26-year-old tech prodigy and Internet activist who was also the co-founder of Reddit, has died. He was found unresponsive in his apartment and was pronounced dead, his family confirms in a statement.

Police have ruled his death one by suicide, TIME magazine reports: Aaron had hanged himself.


“Aaron’s insatiable curiosity, creativity, and brilliance; his reflexive empathy and capacity for selfless, boundless love; his refusal to accept injustice as inevitable – these gifts made the world, and our lives, far brighter,” reads the statement from his family, confirming Swartz’s passing.

“Aaron’s commitment to social justice was profound, and defined his life. He used his prodigious skills as a programmer and technologist not to enrich himself but to make the Internet and the world a fairer, better place,” the family adds.

Swartz was a firm believer that information that benefits the public should be accessible to all, so he concentrated all his efforts into making that happen.

He founded the organization Demand Progress, which was instrumental in getting the US government to back down from the purported anti-piracy law proposed last year.

He also co-founded Reddit, which has turned into one of the biggest platforms for social justice through Internet activist.

A boy wonder, Aaron used his skills to do what he considered was right, even if that meant landing him on the wrong side of the law: in April, he was to stand trial on the charge of federal data theft charge, to which he had already pled not guilty.

According to TIME, Swartz had broken into the “M.I.T. computer system and allegedly download[ed] 4.8 million documents from the subscription based academic research database JSTOR.”

Had he been found guilty, he would have faced a sentence of 35 years in jail and a $1 million (€749,681) fine.

“He was brilliant, and funny. A kid genius. A soul, a conscience, the source of a question I have asked myself a million times: What would Aaron think?” law professor and activist Lawrence Lessig says of Swartz.
Read more

Tuesday, 8 January 2013

Hacker Jailbreaks iPhone 5 Running iOS 6.0.2


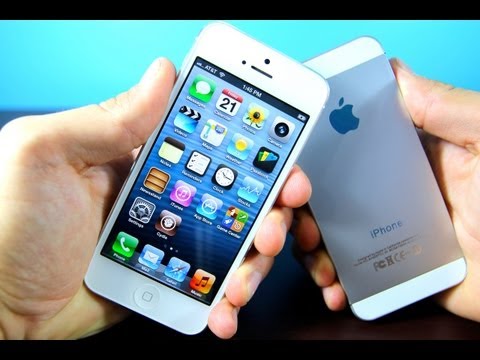
Planetbeing, one of the prominent hackers involved with iOS jailbreaking, takes to Reddit to clear away any confusion regarding the iPhone 5 / iOS 6 jailbreak. In a nutshell, don’t hold your breath for a release until iOS 6.1.

The hacker, well known for his work on past jailbreaks, decided to stop all negative speculation about a potential untethered jailbreak for iOS 6 / iPhone 5.

So he opened a thread on Reddit where he wrote, “Yeah, I'm not really sure what all the doom and gloom is about. The fact is, I have an untethered iOS 6.0.2 JB running on my iPhone 5 right now.”

Had Planetbeing left it at that, the jailbreak community would have been up in arms at this point. Luckily, he didn’t.

“The reasons it's not released are because 1. releasing it would burn an exploit we want to save for ourselves so we can always get in to look at new firmware and help JB in the future, 2. iOS 6.1 is coming very soon and will likely break a small part of it anyway, there's no point in sacrificing the many bugs it won't break,” he explains.

In other words, the hackers cannot afford wasting months of hard work over people’s whining. The release will center on iOS 6.1. Period.

Planetbeing makes a reassuring note, saying, “Anyway, where there are 4+ bugs (that it took to get this to work), there's gotta be one or two more so while jailbreaking is getting harder, reports of its death are highly exaggerated.”

He also explains why he decided to use Reddit instead of Twitter to convey all this to his followers. The gist of it: Twitter’s 140-character limitation.

For who’s asking, iOS 6.1 shouldn’t be too far off with WWDC only six months away. Apple needs to clear developers’ desks of any old software to start focusing on the new stuff.
Read more
 
DMCA.comGags